CVE-2024-26152: falha de média gravidade em HumanSignal label-studio
Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config
Publicada em · Atualizada em
Aviso por e-mail quando ela entrar no KEV, ganhar PoC pública ou subir de nota.
13Vexday Risk Score
Sem sinal de exploração. Nenhum artefato público de exploração conhecido até agora.
ssvc Trackcvss 4.7epss 2.2%
### Summary
On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details
Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project.
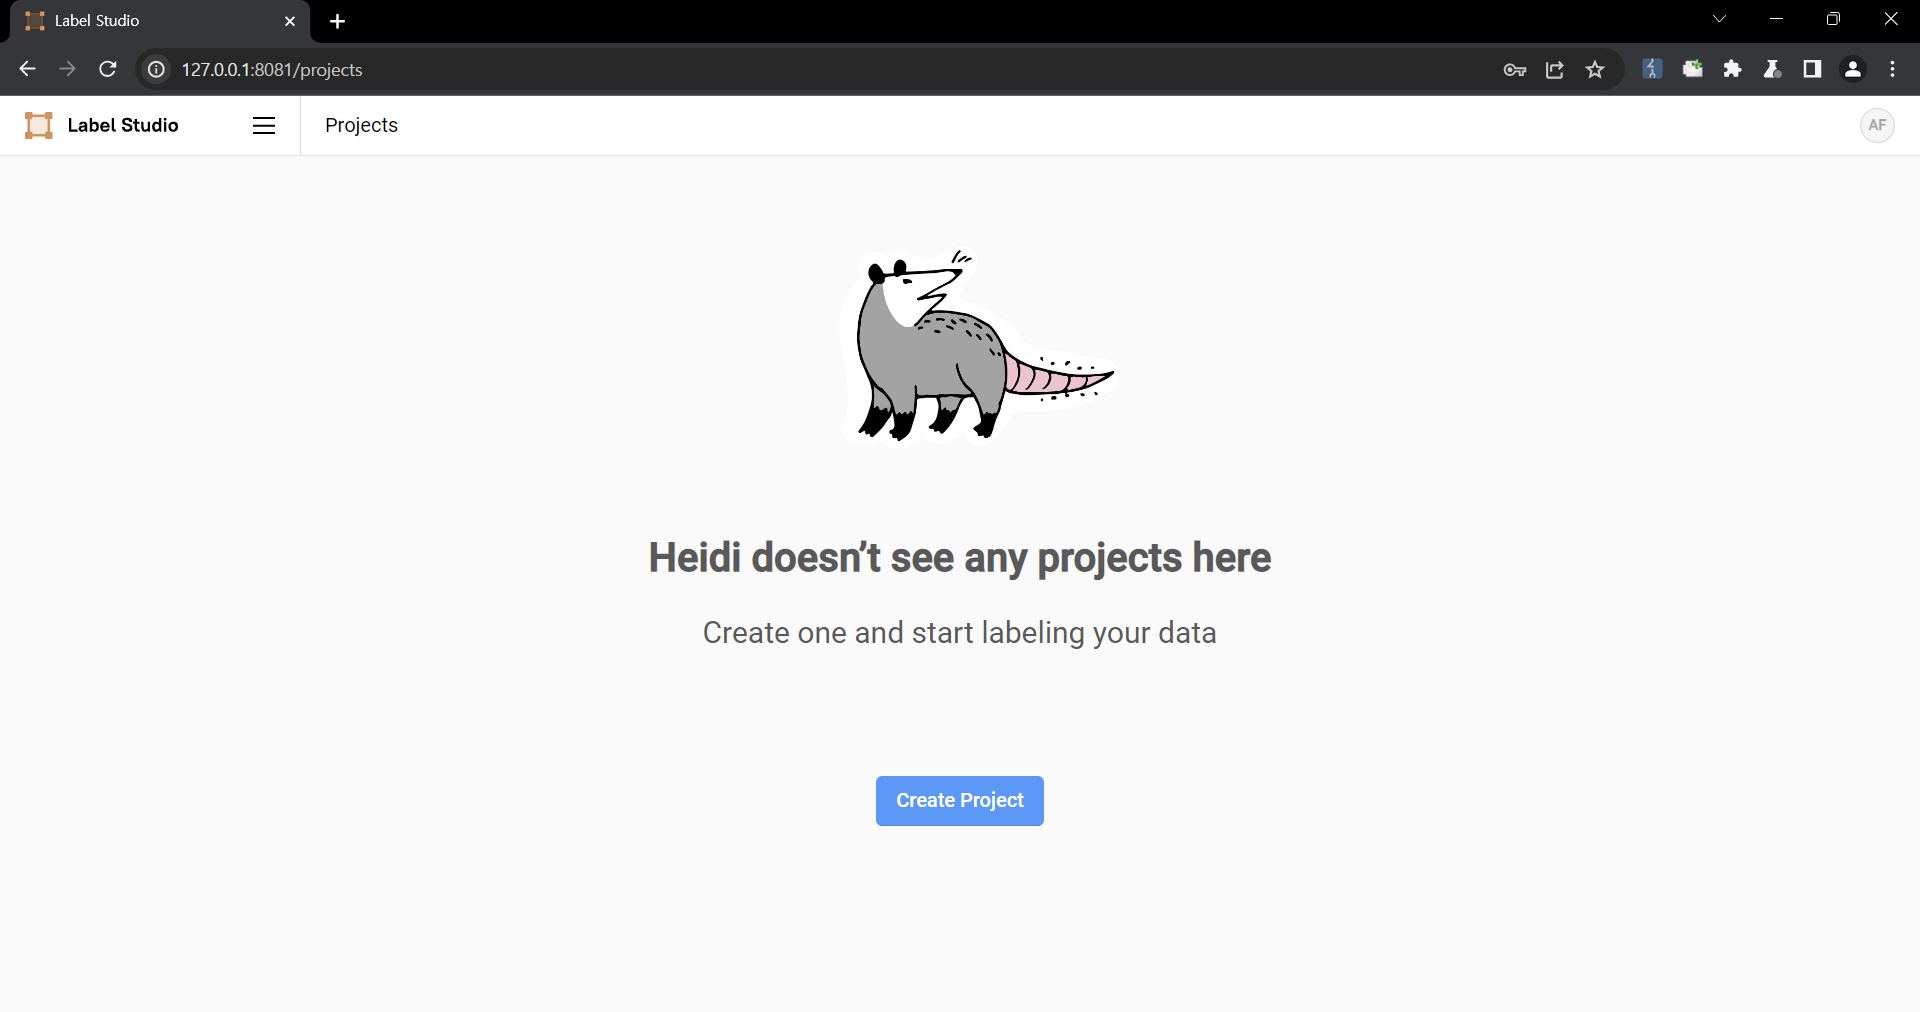
2. Upload a file containing the payload using the "Upload Files" function.
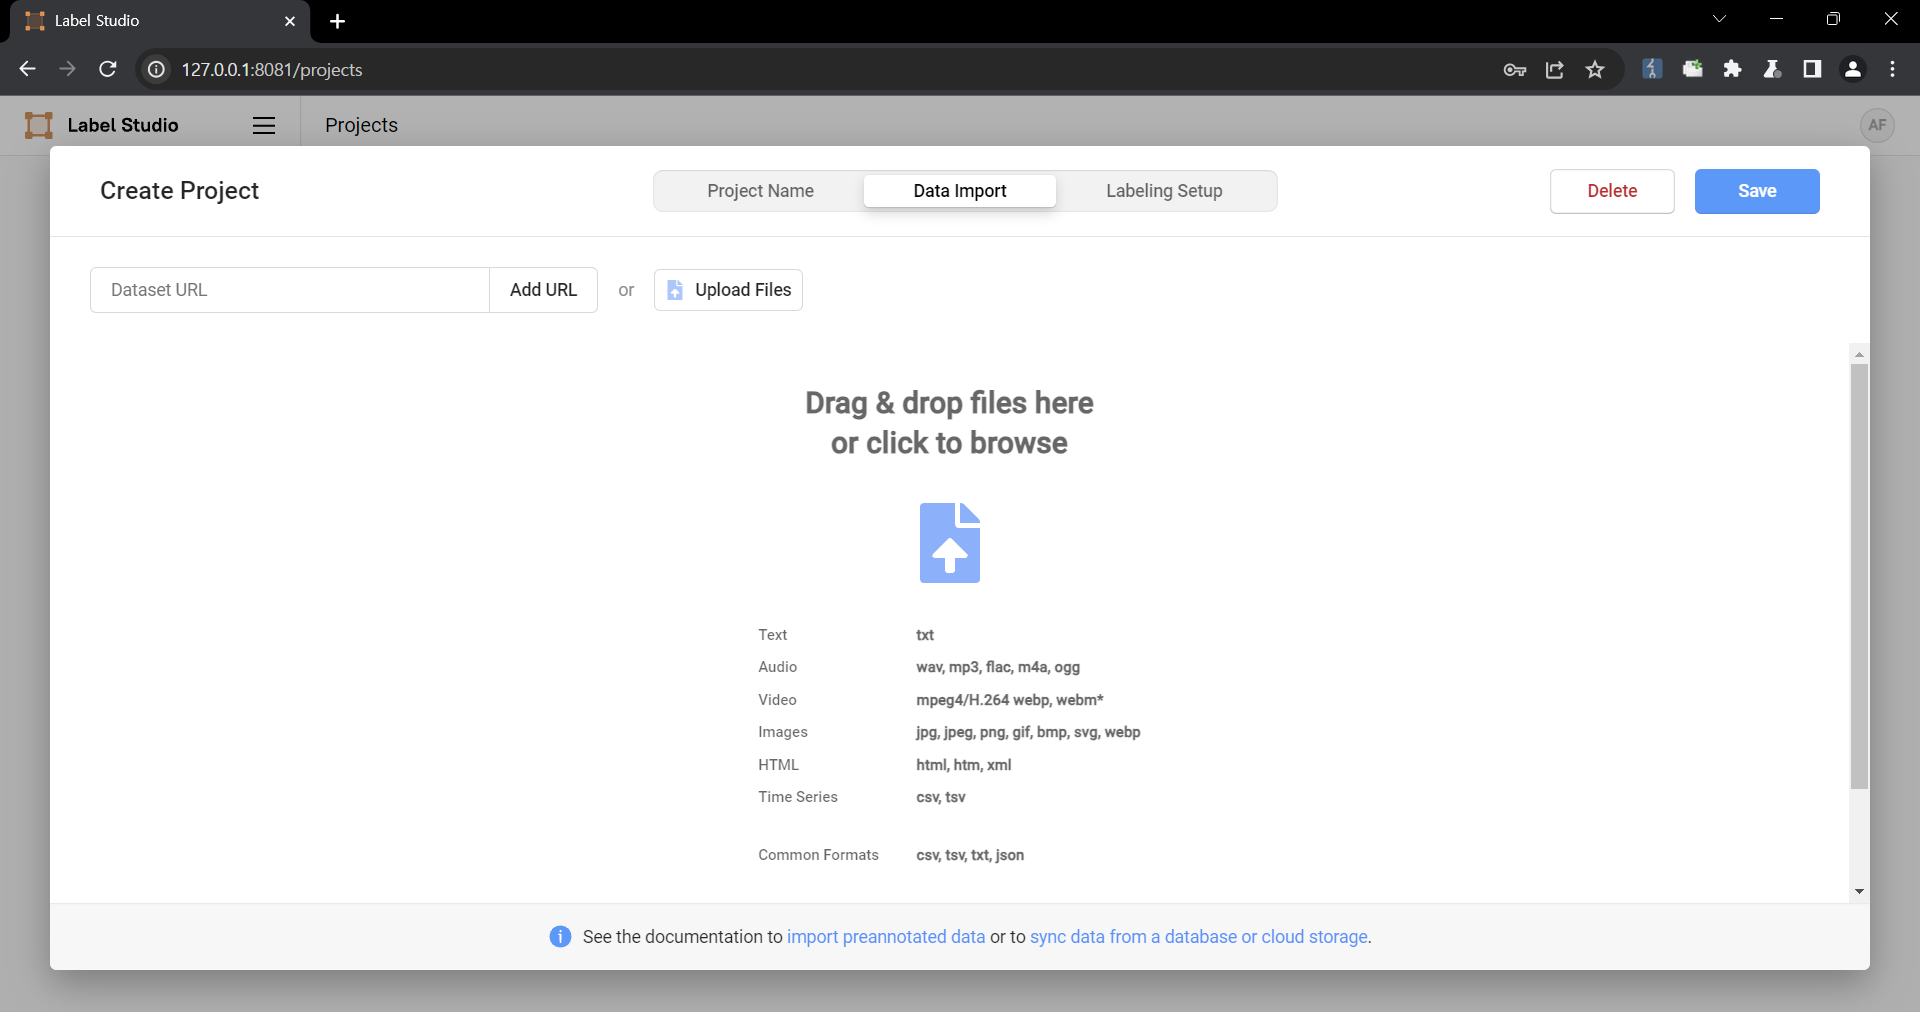
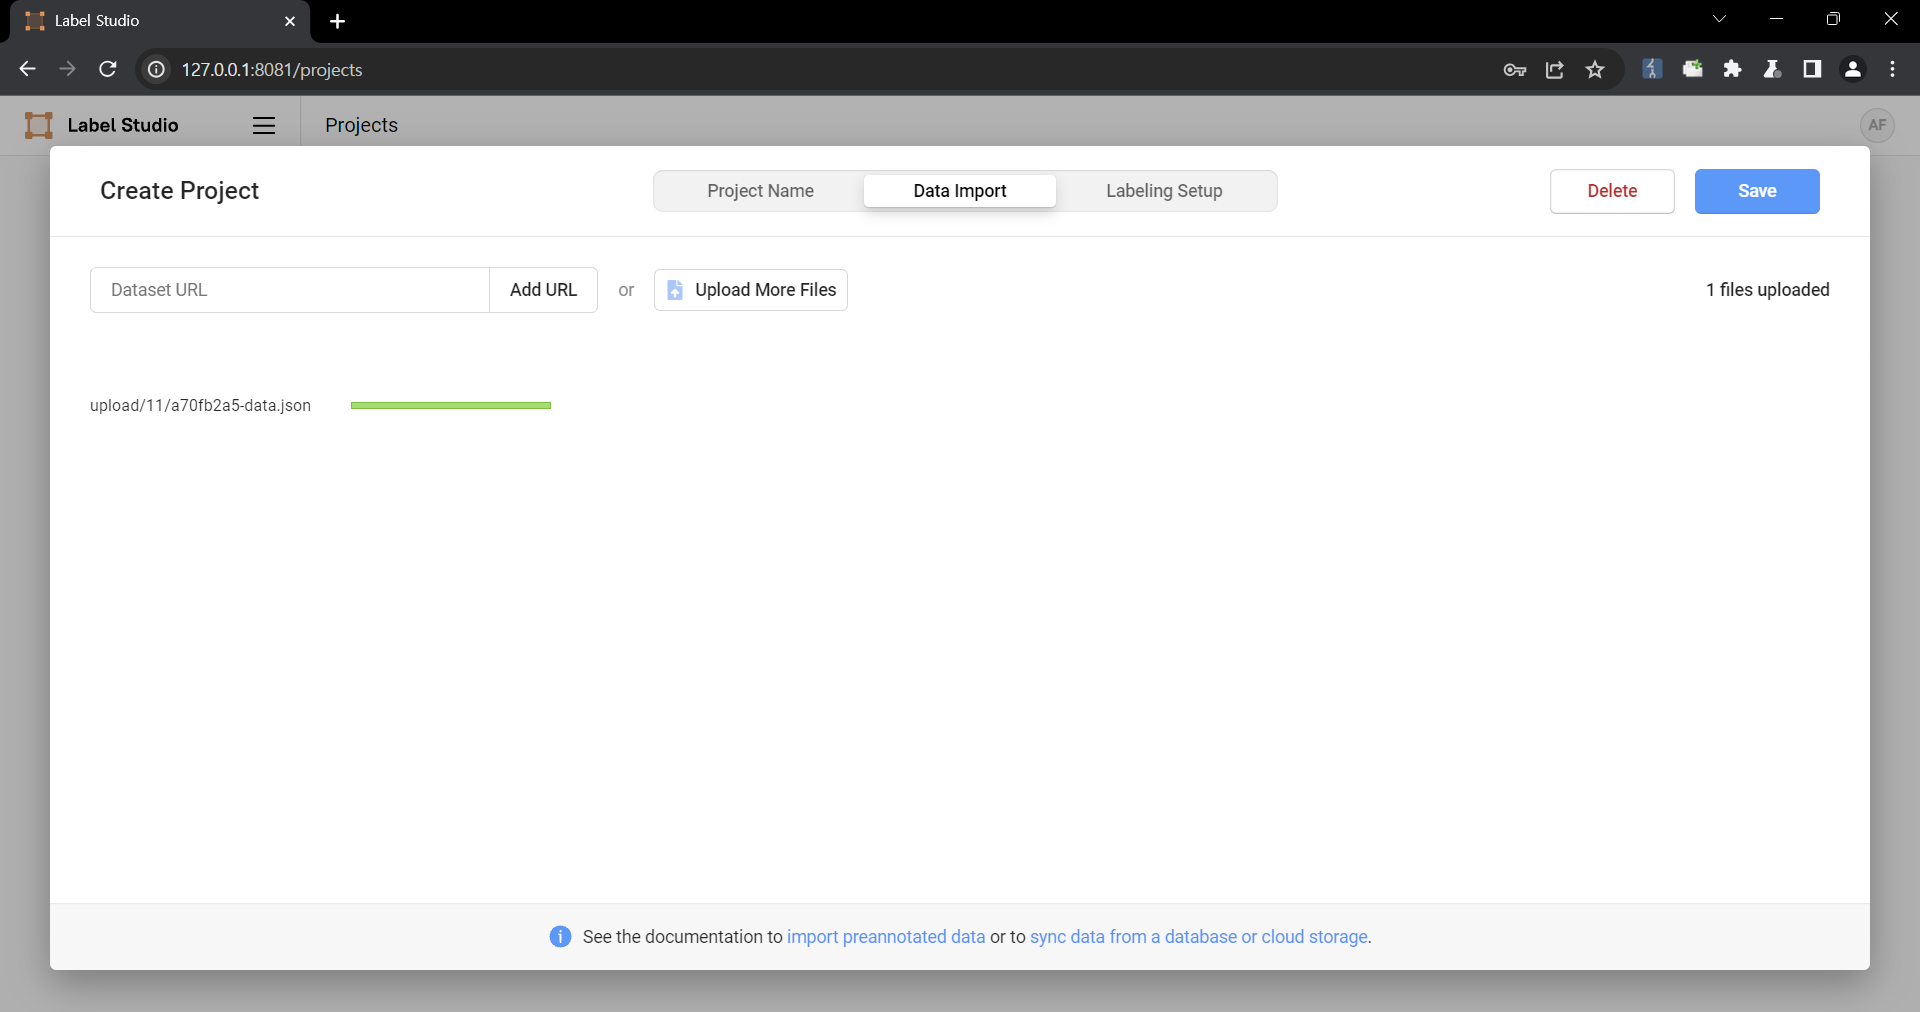
The following are the contents of the files used in the PoC
```
{
"data": {
"prompt": "labelstudio universe image",
"images": [
{
"value": "id123#0",
"style": "margin: 5px",
"html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>"
}
]
}
}
```
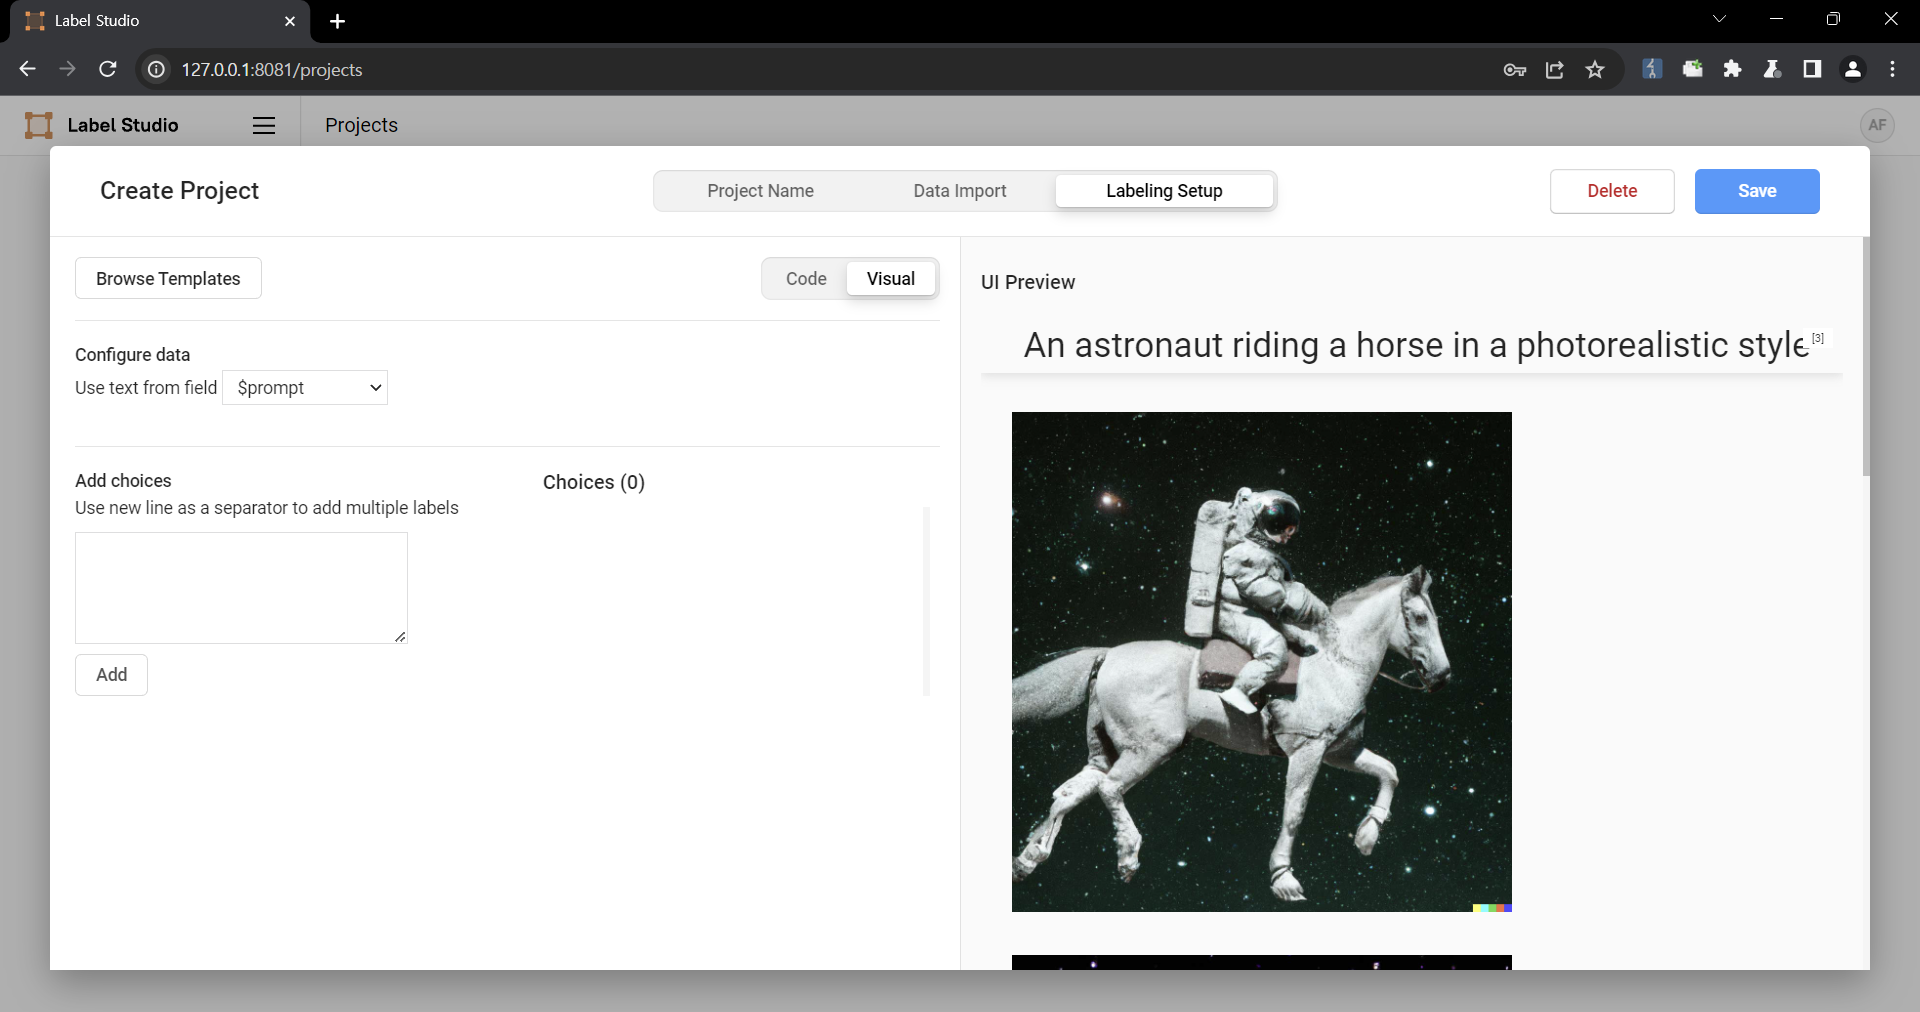
3. Select the text-to-image generation labeling template of Ranking and scoring
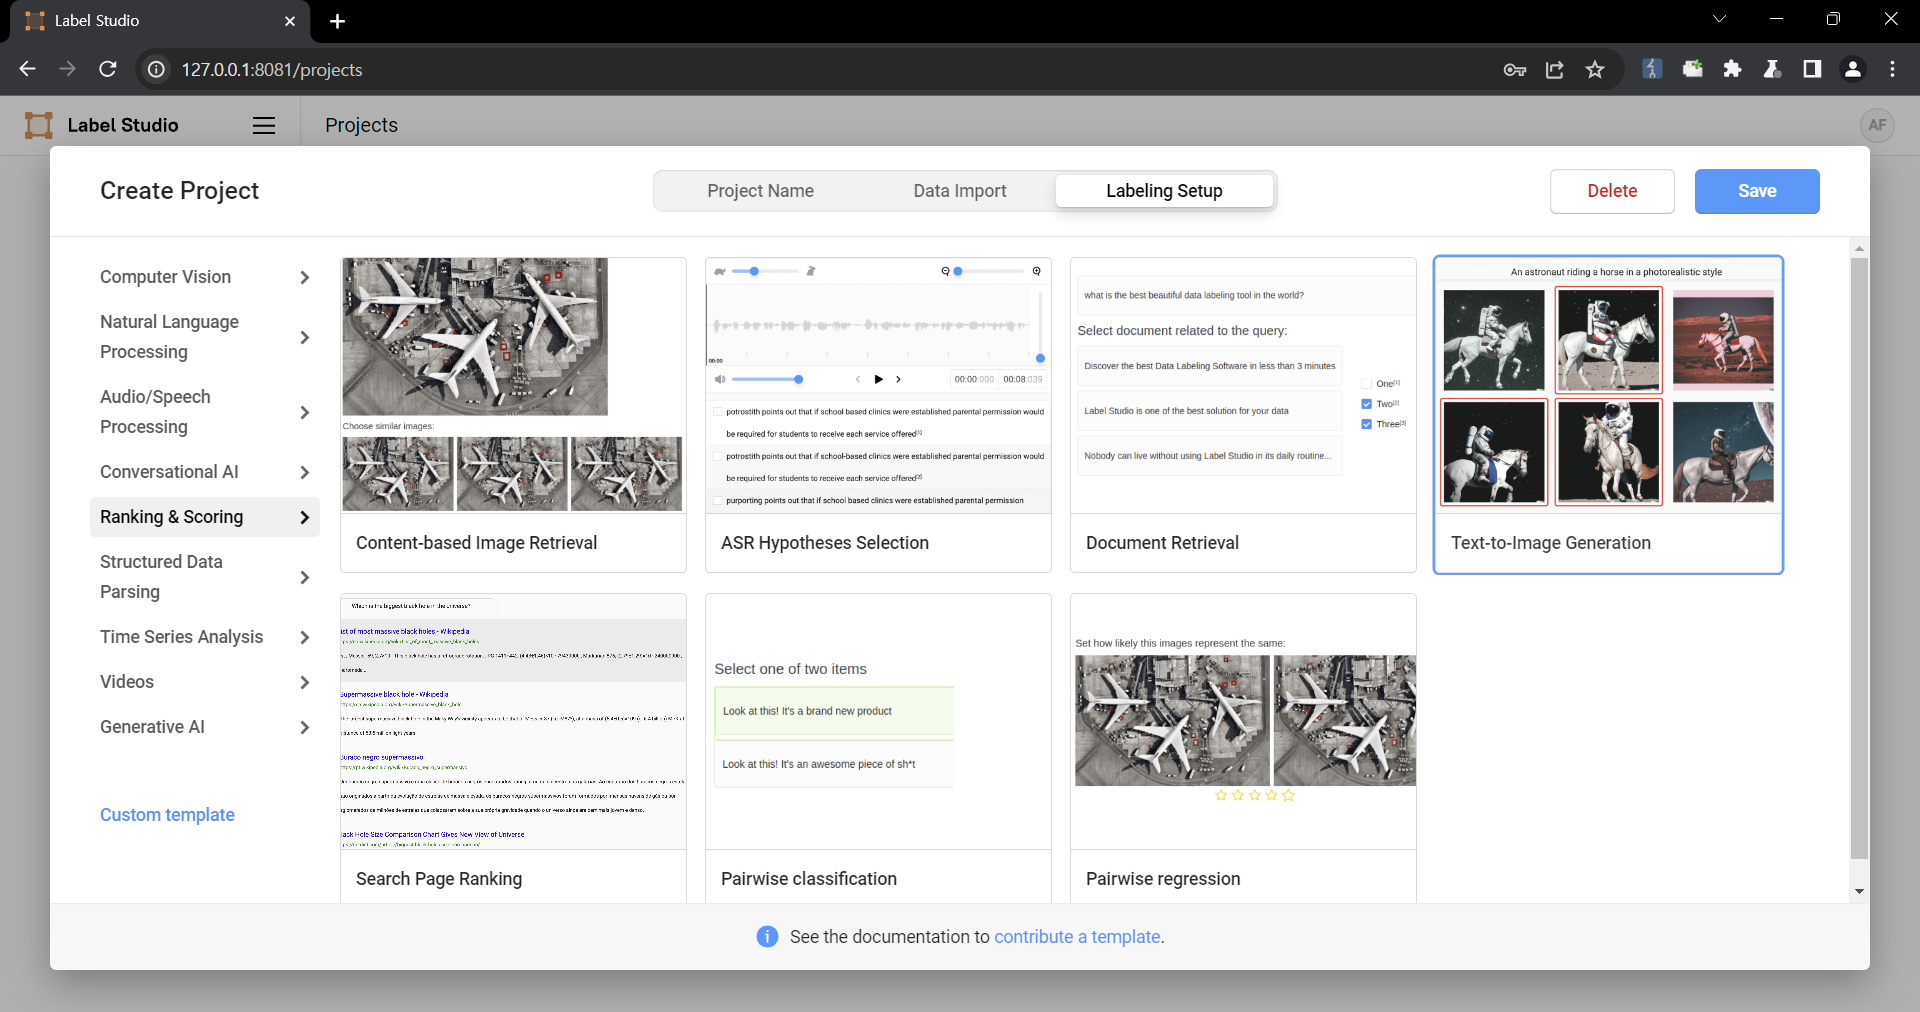
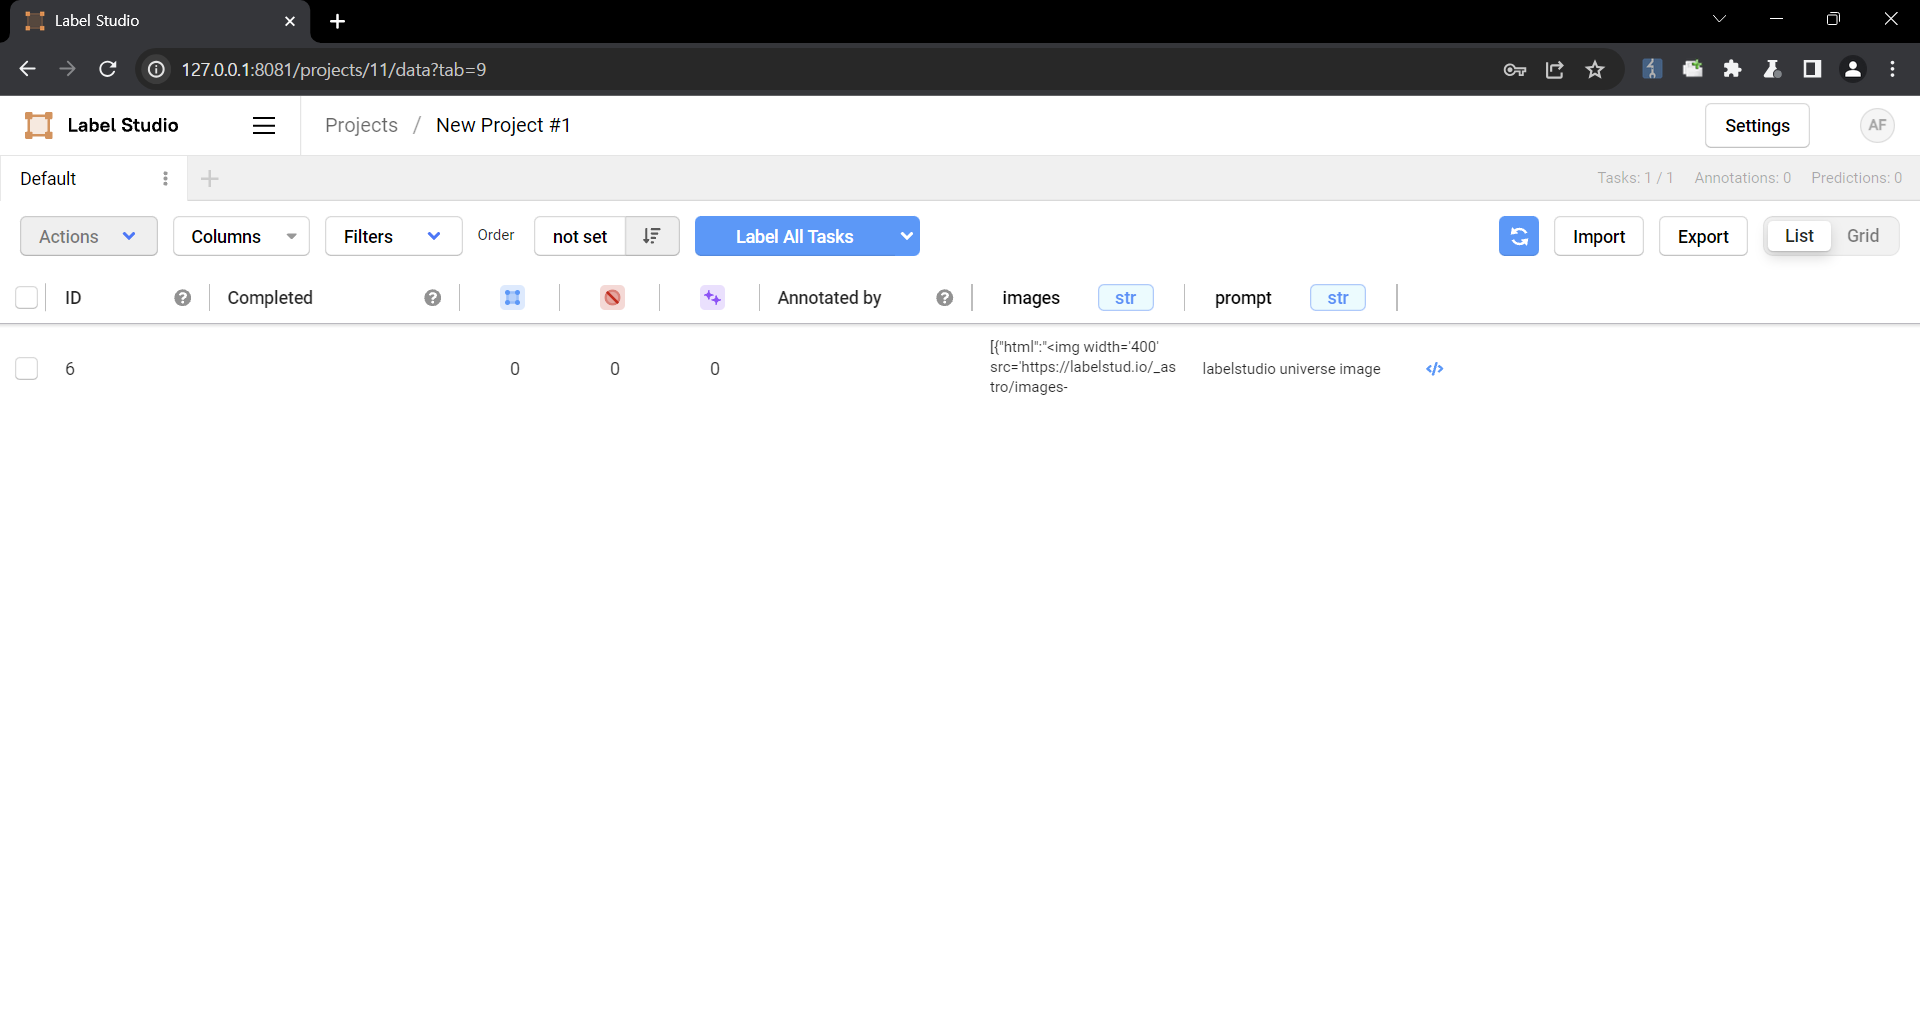
4. Select a task
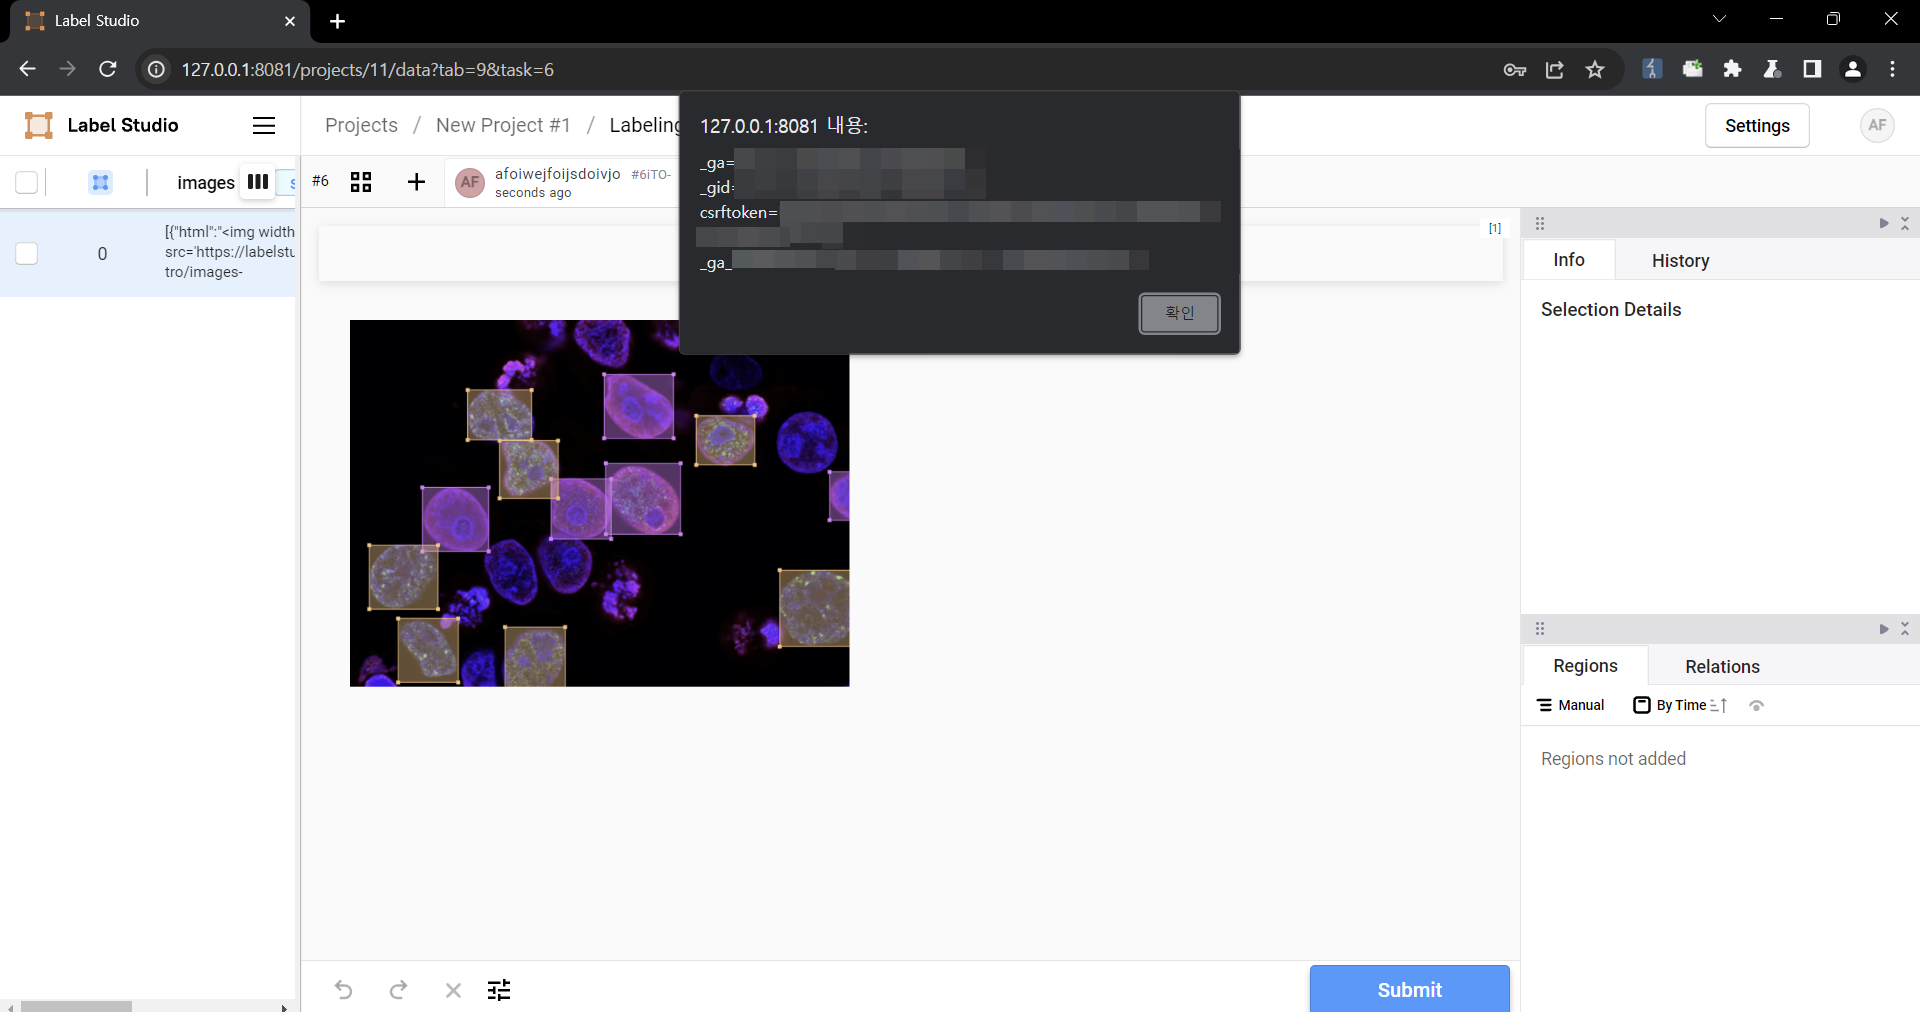
5. Check that the script is running
### Impact
Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N
Produtos afetados
HumanSignal · label-studioCVEs relacionadas — HumanSignal label-studio
No mesmo produto, das mais perigosas para as menos.
CVE-2023-47117HIGHObject Relational Mapper Leak Vulnerability in Filtering Task in Label StudioEPSS 4.1%CVE-2025-25296MEDIUMLabel Studio allows Cross-Site Scripting (XSS) via GET request to `/projects/upload-example` endpointEPSS 1.9%CVE-2023-47115HIGHLabel Studio XSS Vulnerability on Avatar UploadEPSS 1.4%CVE-2023-43791CRITICALLabel Studio has Hardcoded Django `SECRET_KEY` that can be Abused to Forge Session TokensEPSS 1.2%CVE-2025-25295HIGHLabel Studio has a Path Traversal Vulnerability via image FieldEPSS 0.8%CVE-2023-47116MEDIUMLabel Studio SSRF on Import Bypassing `SSRF_PROTECTION_ENABLED` ProtectionsEPSS 0.7%
Referências
https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8https://github.com/HumanSignal/label-studio/pull/5232https://github.com/HumanSignal/label-studio/releases/tag/1.11.0https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg